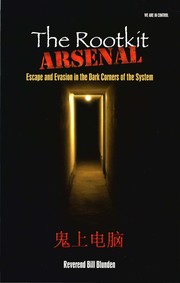
Rootkit arsenal
Bill Blunden · 2012
איפה לקנות
בדקו את המחיר העדכני באמזון. אנחנו לא מציגים מחירים כי הם משתנים מדי יום.
לצפייה באמזוןקישור שותפים. בתור שותפים של Amazon אנחנו מרוויחים מרכישות מתאימות.
על הספר
While forensic analysis has proven to be a valuable investigative tool in the field of computer security, utilizing anti-forensic technology makes it possible to maintain a covert operational foothold for extended periods, even in a high-security environment. Adopting an approach that favors full disclosure, the updated Second Edition of The Rootkit Arsenal presents the most accessible, timely, and complete coverage of forensic countermeasures. This book covers more topics, in greater depth, than any other currently available. In doing so the author forges through the murky back alleys of the Internet, shedding light on material that has traditionally been poorly documented, partially documented, or intentionally undocumented. The range of topics presented includes how to: Evade post-mortem analysis; Frustrate attempts to reverse engineer your command & control modules; Defeat live incident response; Undermine the process of memory analysis; Modify subsystem internals to feed misinformation to the outside; Entrench your code in fortified regions of execution; Design and implement covert channels; Unearth new avenues of attack. - Publisher.
פרטי הספר
- שנה
- 2012
- שפה
- English
- הוצאה
- Jones & Bartlett Learning
- מהדורות
- 1
- עמודים
- 784
- ISBN
- 9781449626365
מקור הנתונים: Wikidata
עוד של Bill Blunden