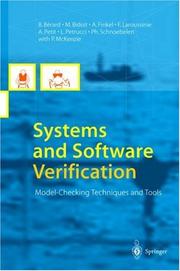
Systems and Software Verification
Béatrice Bérard · 2001
Where to buy
Check today’s price on Amazon. We do not show prices because they change daily.
View on AmazonAffiliate link. As an Amazon Associate we earn from qualifying purchases.
About the book
Model checking is a powerful approach for the formal verification of software. When applicable, it automatically provides complete proofs of correctness, or explains, via counter-examples, why a system is not correct. This book provides a basic introduction to this new technique. The first part describes in simple terms the theoretical basis of model checking: transition systems as a formal model of systems, temporal logic as a formal language for behavioral properties, and model-checking algorithms. The second part explains how to write rich and structured temporal logic specifications in practice, while the third part surveys some of the major model checkers available.
Book details
- Year
- 2001
- Language
- English
- Publisher
- Springer Berlin Heidelberg
- Editions
- 1
- Pages
- 190
- ISBN
- 9783642074783
Data source: Wikidata
More by Béatrice Bérard